
TechfoAnalyzer
18 September 2026
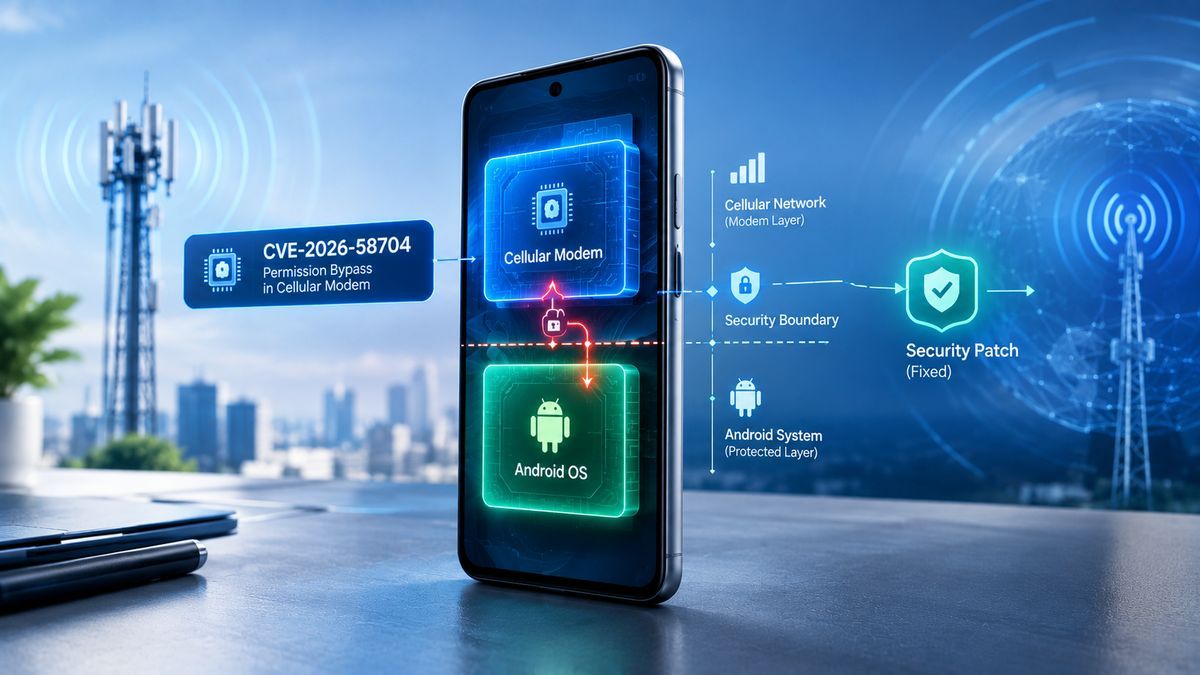
Google Pixel users have a concrete security update to pay attention to this month. Google has patched CVE-2026-58704, a high-severity vulnerability in the cellular modem component of supported Pixel devices, after reporting indications that the flaw may have been used in limited, targeted attacks.
The detail that makes this vulnerability unusual is that Google says exploitation does not require user interaction. In practical terms, the victim does not have to open a malicious file, tap a link, install a suspicious app, or approve a prompt for the vulnerability to be exploited.
That does not mean every Pixel can be hacked remotely from anywhere, though.
Google describes CVE-2026-58704 as an elevation-of-privilege issue caused by a possible permission bypass in the modem, with a remote proximal/adjacent attack vector. The “zero-click” part describes the lack of required victim interaction; it does not mean the attacker faces no other conditions.
That distinction matters because the cellular modem operates below the apps most users interact with. A flaw in that layer can cross a security boundary without looking like a normal Android app attack. At the same time, Google has not publicly disclosed the complete exploit chain, identified the attacker, or provided a victim count. Those gaps make it difficult to say exactly how the real-world attacks worked or how broad they were.
There is a straightforward step you can take. Google says devices with the 2026-09-05 security patch level or later include the September fixes. Check your phone under Settings → About phone → Android version and look at the Android security update level.
Google is rolling the update out in phases, so a missing notification does not necessarily mean the device has been excluded.
CISA's addition of CVE-2026-58704 to its Known Exploited Vulnerabilities catalog adds another important signal that the issue is not merely theoretical. The catalog tracks vulnerabilities with evidence of exploitation. Its remediation deadline applies to U.S. federal civilian agencies, not ordinary Pixel owners around the world, but the listing reinforces why the available security update should not be ignored.
It also helps to understand what “elevation of privilege” does and does not mean. Imagine a phone component that is supposed to have limited authority. If a logic flaw lets that component obtain permissions reserved for a more privileged part of the system, an attacker may gain a stronger position inside the device. That is different from saying the advisory proves complete control of every affected phone.
The issue also does not automatically mean every Pixel owner is currently being targeted. The more defensible takeaway is simpler: this is a patched vulnerability with indications of real-world exploitation, so keeping the device updated matters.
The bigger lesson is easy to miss. Smartphone security is not just about avoiding suspicious links and malicious apps; low-level components such as the modem need security maintenance too. A phone can be carefully used and still depend on software layers the owner never sees.
The remaining questions are technical: exactly how the exploit reached targeted devices, what attackers could do after gaining elevated privileges, and who was responsible. For the full technical context, patch details, attack-vector explanation, and the limits of what is currently known, read the complete analysis on Futuristic Byte. Read the full Futuristic Byte analysis
https://www.futuristicbyte.com/2026/09/cve-2026-58704-pixel.html